

NSE6_FSW-7.2 Dumps PDF 2024 Strategy Your Preparation Efficiently
Latest Verified & Correct Fortinet NSE6_FSW-7.2 Questions
Fortinet NSE6_FSW-7.2 certification is an important credential for network security professionals who work with Fortinet’s FortiSwitch products. It demonstrates the candidate’s expertise in deploying, configuring, and managing secure networks using Fortinet’s technology. Holding this certification can help professionals to advance their careers and increase their earning potential.
The Fortinet NSE 6 - FortiSwitch 7.2 certification exam covers a wide range of topics, including FortiSwitch hardware and software architecture, VLAN configuration, Spanning Tree Protocol (STP), link aggregation, and multicast routing. Candidates will also be tested on their ability to configure FortiSwitch security features, such as access control policies, port security, and network segmentation. NSE6_FSW-7.2 exam consists of multiple-choice questions and simulations, and passing the exam requires a deep understanding of FortiSwitch technologies and their practical applications in real-world scenarios.
NEW QUESTION # 10
Refer to the exhibit.
The profile shown in the exhibit is assigned to a group of managed FortiSwitch ports, and these ports are connected to endpoints which are powered by PoE.
Which configuration action can you perform on the LLDP profile to cause these endpoints to exchange PoE information and negotiate power with the managed FortiSwitch?
- A. Create new a LLDP-MED application type to define the PoE parameters.
- B. Define an LLDP-MED location ID to use standard protocols for power.
- C. Assign a new LLDP profile to handle different LLDP-MED TLVs.
- D. Add power management as part of LLDP-MED TLVs to advertise.
Answer: D
NEW QUESTION # 11
Exhibit.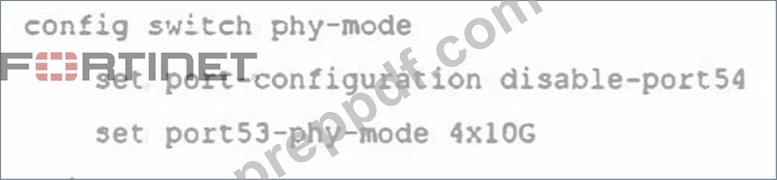
What conditions does a FortiSwitch need to have to successfully configure the options shown in the exhibit above? (Choose two.)
- A. The port full speed prior the split was 100G SFP+
- B. The FortiSwitch model is equipped with a maximum of 54 interfaces.
- C. The split port can be assigned to native VLAN
- D. The CLI commands are enabling a splitpo rt into four 10Gbps interfaces.
Answer: B,D
NEW QUESTION # 12
Which two statements about managing a FortiSwitch stack on FortiGate are true? (Choose two.)
- A. FortiSwitch must be operating in standalone mode before authorization.
- B. A FortiLink interface must be enabled on FortiGate.
- C. The switch controller feature must be enabled on FortiGate.
- D. Only a hardware-based FortiGate can manage a FortiSwitch stack.
Answer: B,C
NEW QUESTION # 13
To enhance service in emergency situations, to which LLDP-MED Type-Length-Values does Forti-Switch advertise to IP phones?
- A. Network policy
- B. Power management
- C. Inventory management
- D. Location
Answer: C
NEW QUESTION # 14
Refer to the exhibit.
What two conclusions can be made regarding DHCP snooping configuration? (Choose two.)
- A. FortiSwitch is configured to trust DHCP replies coming on FortiLink interface.
- B. Global configuration for DHCP snooping is set to forward DHCP client requests on all ports in the VLAN.
- C. Maximum value to accept clients DHCP request is configured as per DHCP server range.
- D. DHCP clients that are trusted by DHCP snooping configured is only one.
Answer: A,D
NEW QUESTION # 15
What feature can network administrators use to segment network operations and the administration of managed FortiSwitch devices on FortiGate?
- A. FortiLink split interface
- B. Multi-chassis link aggregation trunk
- C. FortiGate clustering protocol
- D. FortiGate multi-tenancy
Answer: D
NEW QUESTION # 16
Refer to the diagnostic output: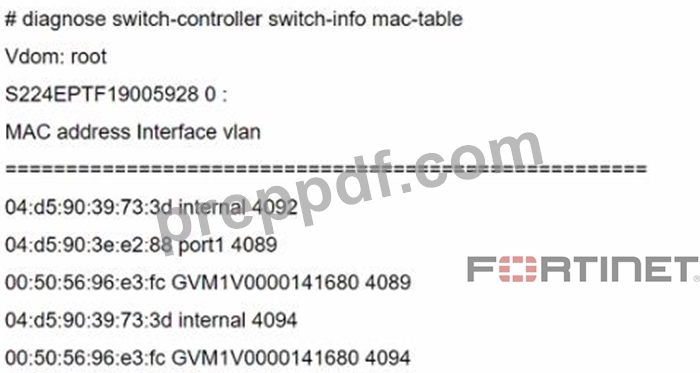
Two entries in the exhibit show that the same MAC address has been used in two different VLANs. Which MAC address is shown in the above output?
- A. It is a MAC address of FortiGate in HA configuration.
- B. It is a MAC address of an upstream FortiSwitch.
- C. It is a MAC address of FortiLink interface on FortiGate.
- D. It is a MAC address of a switch that accepts multiple VLANs.
Answer: D
NEW QUESTION # 17
What can an administrator do to maintain the existing standalone FortlSwltch configuration while changing the management mode to FortLink?
- A. FortiGate will automatically save the existing FortiSwitch configuration during the Forti-link management process.
- B. Register FortiSwitch to For1ISwitch Cloud to save a copy before managing by Forti-Gate.
- C. Use a migration tool based on python script to convert the configuration
- D. Enable the Forti-link setting on FortiSwitch before the authorization process
Answer: D
NEW QUESTION # 18
Which statement about the IGMP snooping querier when enabled on a VLAN is true?
- A. IGMP reports on the VLAN are forwarded to all switch ports.
- B. Active multicast receiver entries are aging on each IGMP query sent on the VLAN
- C. All other indirectly connected switches will be unable to get IGMP multicast traffic.
- D. The setting can only be enabled using the FortiSwitch CLI.
Answer: C
NEW QUESTION # 19
What can an administrator do to maintain a FortiGate-compatible FortiSwitch configuration when changing the management mode from standalone to FortiLinK?
- A. Register FortiSwitch to FortiSwitch Cloud to save a copy before managing with FortiGate.
- B. Use a migration tool based on Python script to convert the configuration.
- C. Enable the FortiLink setting on FortiSwitch before the authorization process.
- D. FortiGate automatically saves the existing FortiSwitch configuration during the FortiLink management process.
Answer: A
NEW QUESTION # 20
How are the 'by VLAN redirect MAC address quarantine' mode and the 'by redirect MAC address quarantine' mode on FortiGate similar?
- A. Both modes require firewall policies to block inter-VLAN traffic.
- B. Both modes block intra-VLAN traffic by FortiGate automatically.
- C. Both modes move quarantined devices to the quarantine VLAN.
- D. Both modes add quarantined device MAC addresses to the blocked firewall address group.
Answer: B
NEW QUESTION # 21
Refer to the diagnostic output: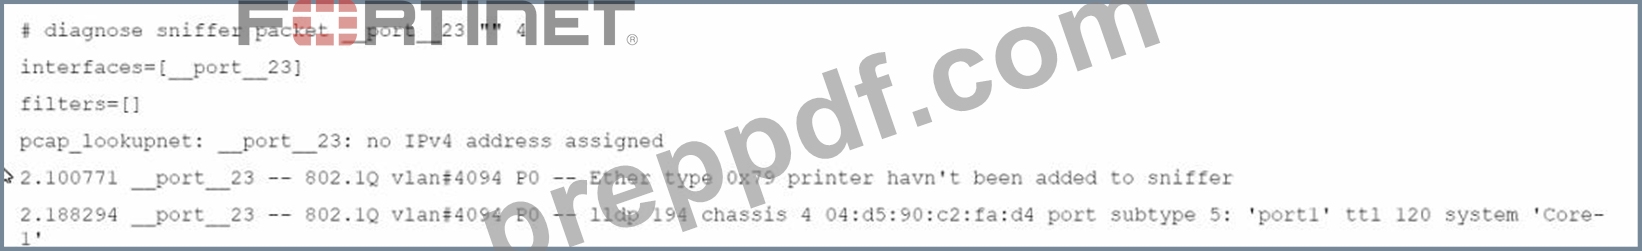
What makes the use of the sniffer command on the FortiSwitch CLI unreliable on__port__23?
- A. The types of packets captured is limited.
- B. Only untagged VLAN traffic can be captured.
- C. The switch port might be used as a trunk member
- D. Just the port egress payloads are printed on CLI.
Answer: A
NEW QUESTION # 22
Refer to the exhibits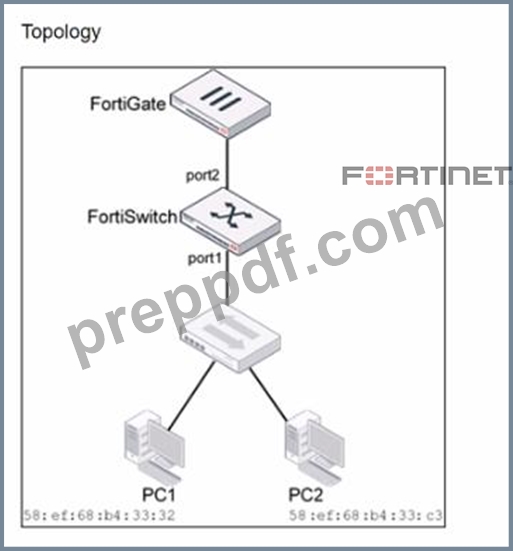
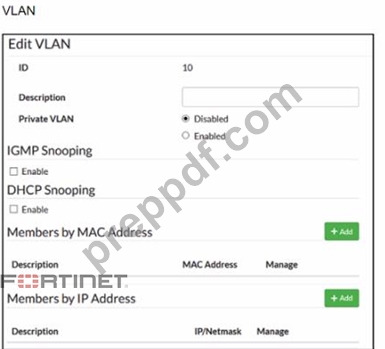
Traffic arriving on port2 on FortiSwitch is tagged with VLAN ID 10 and destined for PC1 connected on port1. PC1 expects to receive traffic untagged from port1 on FortiSwitch.
Which two configurations can you perform on FortiSwitch to ensure PC1 receives untagged traffic on port1? (Choose two.)
- A. Add VLAN ID 10 as a member of the untagged VLANs on port1.
- B. Add the MAC address of PCI as a member of VLAN 10.
- C. Remove VLAN 10 from the allowed VLANs and add it to untagged VLANs on port1.
- D. Enable Private VLAN on VLAN 10 and add VLAN 20 as an isolated VLAN.
Answer: A,B
NEW QUESTION # 23
How does FortiSwitch perform actions on ingress and egress traffic using the access control list (ACL)?
- A. FortiSwitch checks ACL policies only from top to bottom.
- B. Only high-end FortiSwitch models support ACL.
- C. ACL can be used only at the prelookup stage in the traffic processing pipeline.
- D. Classifiers enable matching traffic based only on the VLAN ID.
Answer: A
NEW QUESTION # 24
Exhibit.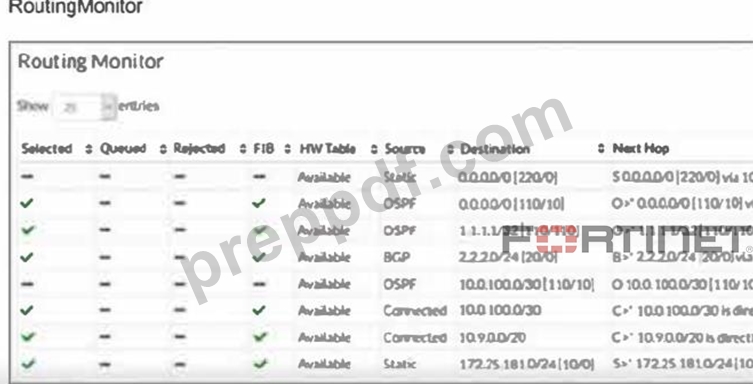
Two routes are not installed in the forwarding information base (FIB) as shown in the exnibit. Which two statements about these two route entries are true? (Choose two.)
- A. These two routes will become primary, if the best routes are removed.
- B. These two routes are available in the hardware routing table.
- C. These two routes have a higher administrative distance value available to the destina-tion networks.
- D. These two routes will be used as load-balancing routes.
Answer: A,C
NEW QUESTION # 25
Which statement about the quarantine VLAN on FortiSwitch is true?
- A. It is only used for quarantined devices if global setting is set to quarantine by VLAN.
- B. Quarantine VLAN has no DHCP server
- C. FortiSwitch can block devices without configuring quarantine VLAN to be part of the allowed VLANs.
- D. Users who fail 802.1X authentication can be placed on the quarantine VLAN.
Answer: A
NEW QUESTION # 26
Which two statements about DHCP snooping enabled on a FortiSwitch VLAN are true? (Choose two.)
- A. Settings related to DHCP option 82 are only configurable through the CLI
- B. switch-controller-dhcp-snooping-verify-mac verifies the destination MAC address to protect against DHCP exhaustion attacks.
- C. By default, all FortiSwitch ports are set to forward client DHCP requests to untrusted ports.
- D. Enabling DHCP snooping on a FortiSwitch VLAN ensures requests and replies are seen by all DHCP servers.
Answer: A,C
NEW QUESTION # 27
Which drop policy mode, if assigned to a congested port, will drop incoming packets until there is no congestion on the egress port?
- A. Tail-drop mode
- B. Weighted round robin mode.
- C. Strict mode
- D. Random early detection mode
Answer: A
NEW QUESTION # 28
What type of multimode transceiver can be used to split a 40G port?
- A. QSFP+ transceiver
- B. QSFP transceiver
- C. SFP+ transceiver
- D. SFP transceiver
Answer: A
NEW QUESTION # 29
Which statement about the use of the switch port analyzer (SPAN) packet capture method is true?
- A. SPAN can be configured only on a standalone FortiSwitch.
- B. Traffic on the management interface can be mirrored and captured by the monitoring device.
- C. The monitoring device must be connected to the same switch where the traffic is being mirrored
- D. Mirrored traffic can be sent across multiple switches.
Answer: B
NEW QUESTION # 30
Which two statements about the FortiLink authorization process are true? (Choose two.)
- A. The administrator must manually pre-authorize FortiGate on FortiSwitch by adding the FortiGate serial number.
- B. A FortiLink frame is sent by FortiGate to FortiSwitch to complete the authorization.
- C. FortiSwitch requires a reboot to complete the authorization process.
- D. FortiLink authorization sets the FortiSwitch management mode to FortiLink.
Answer: B,D
NEW QUESTION # 31
......
NSE6_FSW-7.2 PDF Dumps Are Helpful To produce Your Dreams Correct QA's: https://passcertification.preppdf.com/Fortinet/NSE6_FSW-7.2-prepaway-exam-dumps.html